insurance vendor access recertification: key takeaways
Vendor permission review is stronger when the account, data scope, business purpose, owner, expiration rule, and current evidence are explicit.
- Inventory vendor identities and access scope.
- Tie permission to a current business purpose.
- Record recertification evidence and exceptions.
- Escalate security and contractual decisions to the authorized owner.
Research plan dated 2026-08-21
This review tests whether official sources provide a defensible benchmark for insurance vendor access recertification. It keeps reported figures separate from local operating measures.
- Sample vendor accounts by system, scope, age, and owner.
- Compare permissions with current contract, purpose, and active work.
- Classify confirmed, stale, excessive, orphaned, and disputed access.
- Test whether a reviewer can explain the disposition without relying on memory.
insurance vendor access recertification: what the current data says
A vendor account can remain active after a project ends, while an access review can also remove a permission that a current service depends on. Recertification studies both sides of that evidence problem.
Research question. Can an insurance agency show that a vendor still needs a particular permission, rather than treating an active account or familiar supplier as proof of continuing access? Vendor access can support document exchange, client communication, claims coordination, accounting, or technology maintenance. The access may be legitimate and still need a narrow scope, an expiration date, a named owner, and evidence that the business purpose remains current.
Define the unit as an identity-permission pair. One vendor may have several users, systems, roles, and environments. One user may support multiple services. Record identity, vendor, system, role, data category, action scope, business purpose, contract or work reference, owner, creation date, last-use evidence, and review date. An account-level approval hides which permission was actually examined.
Start with the source of access. Preserve the request, approval, contract clause, ticket, system record, and any exception. Distinguish access granted for a project from access granted for ongoing support. A current invoice or active contract may show a commercial relationship but not the exact data or action scope. A vendor's name in an address book is not permission evidence.
Classify the current state as confirmed necessary, necessary but overbroad, stale, orphaned, disputed, or unable to verify. Record the evidence and the disposition. ‘No longer used’ may be supported by system activity, project closure, or owner confirmation, but absence of recent activity alone is not proof that access is unnecessary. Conversely, a recent login does not prove that every available permission is needed.
Study least-privilege questions concretely. Can the vendor receive documents without deleting them? Can it view a client record without exporting unrelated records? Can a service account be limited to one workflow? Can temporary access expire automatically? These are questions about scope and control design. They are not instructions to a non-authorized worker to make a security or contractual judgment outside written policy.
Include difficult cases: shared mailboxes, service accounts, subcontractors, emergency access, departed vendor personnel, merged systems, and accounts with no clear owner. These cases often reveal whether an agency can prove permission purpose. A sample containing only individually named active users may show an ideal state rather than operational reality.
Reconcile four records: the access inventory, source approval, current work purpose, and system permission state. Check names, roles, dates, data categories, and action capabilities. Preserve evidence of changes, including permission reduction, disablement, owner reassignment, or exception approval. A later removal should not erase the earlier reason an account was difficult to verify.
CISA guidance supports identity, access, and response control thinking, but it does not certify a local program. NAIC material provides insurance market-conduct context, not a vendor-access pass rate. ACORD standards help frame data exchange, not authorization. BLS occupational data describes clerical roles, not security responsibility. Keep those facts separate from local observations and from any legal or contractual conclusion.
Measure recertification evidence rather than only the number of accounts reviewed. Count identity-permission pairs with a current owner, purpose, source approval, scope description, review date, and disposition. Track orphaned accounts, excessive scope, missing evidence, exception age, and time to disable after confirmed offboarding. Report system and vendor mix. A high review count can coexist with weak evidence if every account is simply marked active.
Use a blind reviewer reconstruction. Give a reviewer the access record, approval, current work reference, scope, activity evidence, and disposition without a verbal explanation. Ask why access exists, what data it reaches, who can authorize change, and what remains uncertain. The result evaluates auditability and handoff quality, not whether the system is secure in every respect.
Limitations include incomplete logs, subcontractor relationships, emergency procedures, inconsistent role naming, contract changes, and systems that cannot express narrow permissions. This method cannot establish a cybersecurity certification, legal compliance, breach status, or vendor trustworthiness. It can show whether permission purpose and review evidence are visible enough for the authorized owner to act.
Recertification should record the decision horizon. A permission may be necessary for a project that ends next month, acceptable only until a migration, or required continuously for a contracted service. The review should name the next review date and the event that would trigger earlier reassessment, such as offboarding, contract change, system replacement, or a change in data scope. This turns a one-time confirmation into a bounded control record. It does not mean a researcher can approve access; it means the authorized owner receives enough evidence to approve, reduce, disable, or investigate the permission with a clear reason.
Reviewers should distinguish an access decision from an evidence decision. The study can say that the record supports, fails to support, or leaves uncertain a permission claim. It should not silently convert that finding into an instruction to disable an account. The authorized owner may need to consider service continuity, incident response, contract terms, privacy, and system dependencies before changing access.
Evidence-led conclusion. Vendor access recertification is defensible when each identity-permission pair has a current purpose, narrow scope, accountable owner, source approval, review evidence, and explicit exception path. Active access is not proof of need, and inactivity is not proof of irrelevance. InsuranceYo can research and organize that evidence chain while leaving security, contractual, and system-authority decisions with the designated owners. The study does not replace an authorized security review or a documented incident process. It makes the permission evidence and its limits easier to inspect during a repeatable review.
A safe role design separates advice and authority from documented administration. Support staff can collect records, update systems, prepare work, and maintain follow-ups under written procedures. Licensed staff remain responsible for coverage discussions, recommendations, approvals, and any activity restricted by law or carrier agreement.
Consolidated statistics
Screenshot-ready table. Verified August 21, 2026. These figures are benchmarks and context, not an observed industry average or a modeled scenario.
| Source | Metric | Published value | Geography and population | Date | Caveat |
|---|---|---|---|---|---|
| NAIC Market Conduct Annual Statement | Regulatory context | Market-conduct reporting framework | United States insurance regulation | Reference checked August 21, 2026 | A reporting framework is not an agency performance benchmark. |
| ACORD Property and Casualty Data Standards | Data exchange context | P&C data standards documentation | Insurance data exchange | Reference checked August 21, 2026 | A standard does not prove that a local record is complete or correct. |
| BLS Occupational Outlook Handbook, Financial Clerks | Occupation context | Insurance claims and policy processing clerks | United States labor market | 2024 employment and May 2024 wage data | Occupation data does not measure an agency's queue, quality, or staffing need. |
| CISA Cybersecurity Performance Goals | Control context | Identity, access, and response practices | United States guidance | Reference checked August 21, 2026 | Guidance is not proof that an agency has implemented a control. |
Workflow and controls
| Stage | Control |
|---|---|
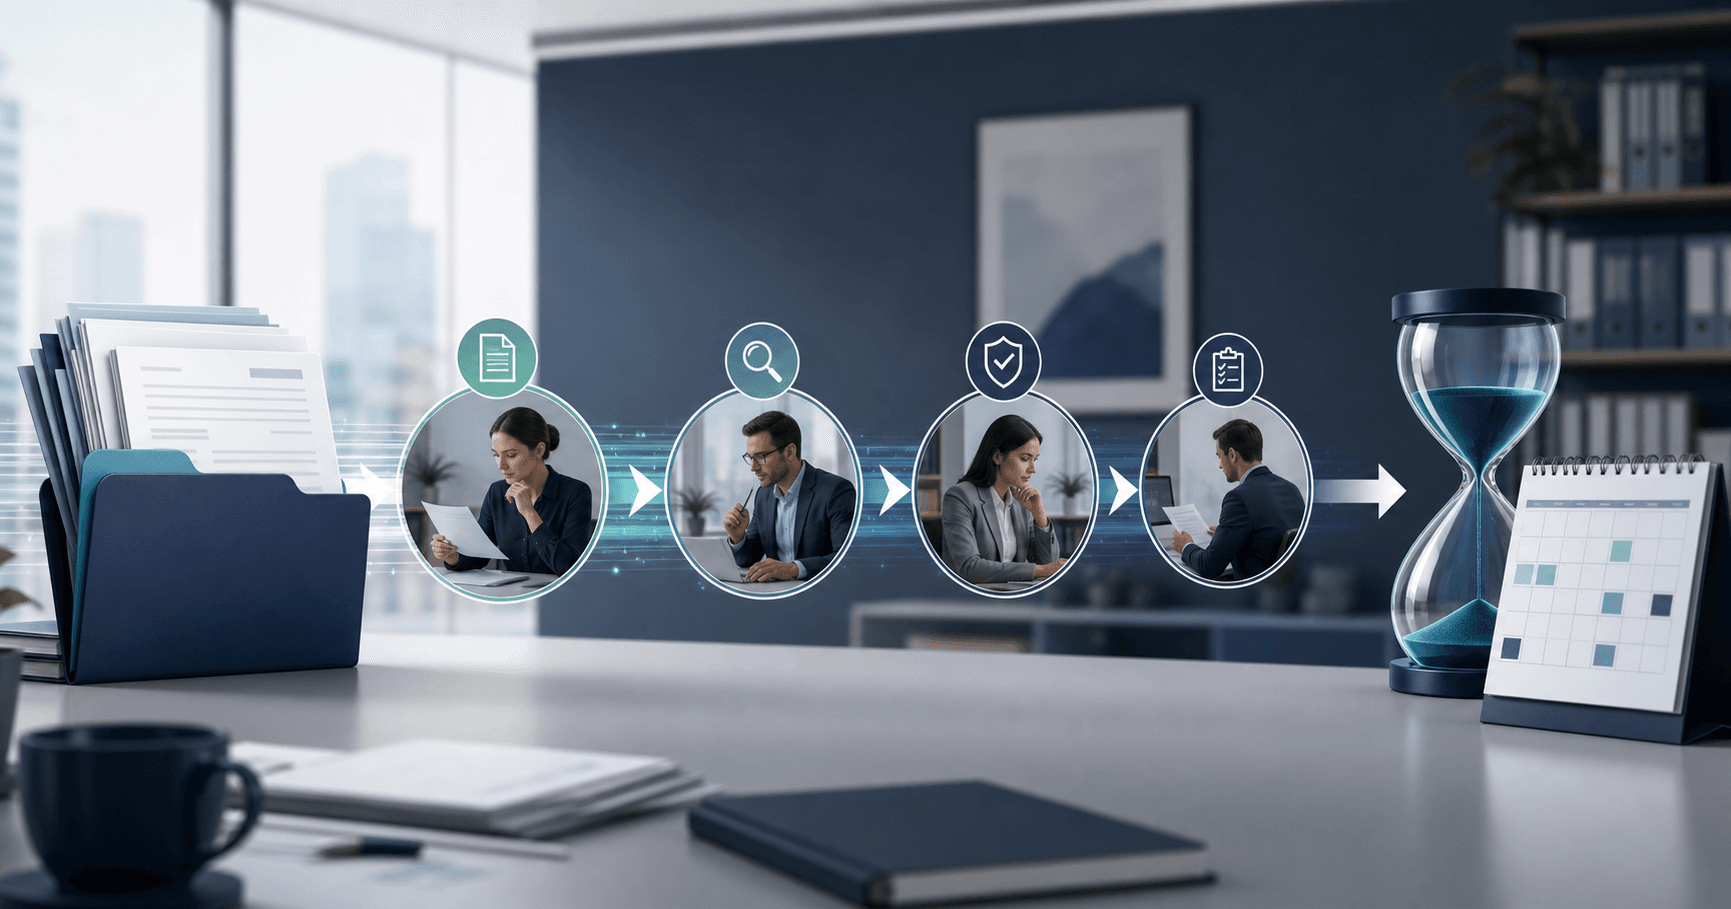
| 1 | Inventory vendor identities and access scope. |
| 2 | Tie permission to a current business purpose. |
| 3 | Record recertification evidence and exceptions. |
| 4 | Escalate security and contractual decisions to the authorized owner. |
Sources and method
Methodology (verified August 21, 2026; 2026-08-21): one observation is a vendor identity and permission set linked to system, scope, purpose, contract or work reference, last use, reviewer, recertification date, and disposition. External context includes CISA Cybersecurity Performance Goals (https://www.cisa.gov/cybersecurity-performance-goals), NAIC Market Conduct Annual Statement (https://content.naic.org/insurance-topics/market-conduct-annual-statement), ACORD Property and Casualty Data Standards (https://www-dev.acord.org/standards-architecture/acord-data-standards/Property_Casualty_Data_Standards), and BLS Financial Clerks data (https://www.bls.gov/ooh/office-and-administrative-support/financial-clerks.htm). These sources do not certify local security or contractual compliance.
- NAIC Market Conduct Annual Statement, Reference checked August 21, 2026.
- ACORD Property and Casualty Data Standards, Reference checked August 21, 2026.
- BLS Occupational Outlook Handbook, Financial Clerks, 2024 employment and May 2024 wage data.
- CISA Cybersecurity Performance Goals, Reference checked August 21, 2026.
Frequently asked questions
What does this study establish?
It establishes a permission-evidence study method, not a cybersecurity certification or legal compliance finding.
Do national labor figures predict one agency's cost?
No. They are benchmarks. Location, role mix, benefits, tools, management, and workload determine actual cost.
Which work should stay with licensed staff?
Coverage advice, recommendations, binding authority, and regulated activity should remain with properly licensed and authorized staff.
Want to map this workload in your agency?
InsuranceYo can help separate licensed decisions from documented support work and outline a practical staffing plan.
Talk through your workflow